this week in security — november 15 2026 edition
THIS WEEK, TL;DR
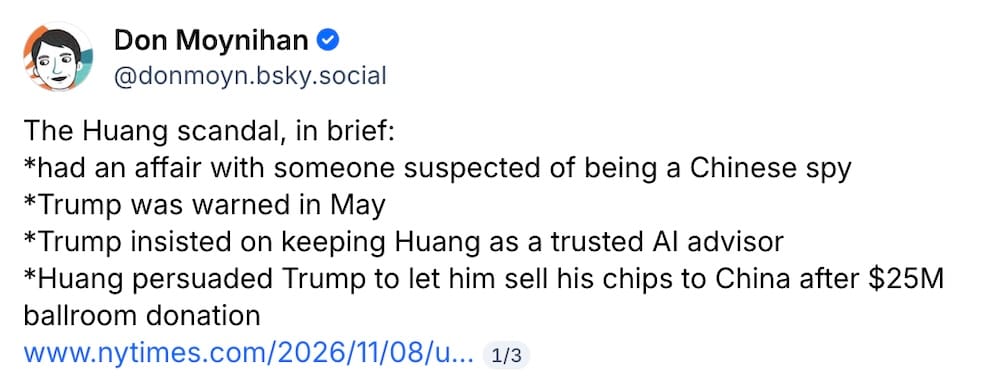
Nvidia's Jensen Huang resigns amid affair with alleged Chinese spy, sparking national security concerns
Associated Press: *spits out tea* Jensen Huang did potentially what?! Yes, in case you missed it, the Nvidia founder is out as its chief executive after admitting to an affair with someone suspected of spying for China. Nvidia wanted Huang out after U.S. intelligence linked Alice Huang (of no relation) to China's security services. Nvidia says there's no evidence that any sensitive information was shared. But this also blew up because the U.S. government, which has been trying to prevent Nvidia-made chips from getting to China's military, had made no effort to add several companies suspected of diverting chips to China to the U.S. government's own economic blocklist aimed at preventing such transfers. Nobody's quite sure exactly why (just yet...), but Reuters ($) and Axios report that Commerce Secretary Howard Lutnick, a close friend of Trump's, might be in the firing line, as it's ultimately his department that handles the government's blocklist. What started as an unfaithful Nvidia executive spiraled into a massive national security scandal. Expect this story to stick around as Huang is likely to testify to lawmakers. Also, solid reporting from Reuters ($) on the security teams behind executive protection.
More: Nvidia | The New York Times ($) | Bloomberg ($) | WSJ ($) | The Verge ($) | The Guardian | CNN | PBS | Engelsberg Ideas | emptywheel | @sarahjeong | @swin24
Cursor, Notion, and Uber confirm data breaches following hack at Fireworks AI
Bloomberg ($): Fireworks AI, a company that allows developers to run AI models, was hacked twice in recent months by financially motivated cybercriminals, who used internal credentials to gain access to some customers' data stored on its servers, including secrets and datasets. Several Fireworks' customers are known to have been hacked in the fallout, including document editor Notion, and I also reported for TechCrunch ($) that Uber had thousands of its drivers' licenses stolen in a breach linked to Fireworks (disclosure alert!). Cursor also confirmed that an earlier breach that allowed hackers to distribute a malicious Claude Code extension through its marketplace was caused by the Fireworks breach. Oh: And Don't miss Railway's post-mortem, which allowed a hacker to break into around ~100,000 workspaces; with additional analysis from Forte Platforms.
More: Fireworks AI | Forbes ($) | The Register | Bleeping Computer
Microsoft fixes nearly 1,100 flaws, amid mixed views on AI's overall helpfulness
Krebs on Security: Microsoft has fixed a whopping 1,093 or so vulnerabilities in this month's Patch Tuesday, with dozens rated "critical" and one known zero-day under attack. Microsoft credited AI in its recent waves of codebase-cleanups, allowing the company (among others) to patch flaws that might have otherwise gone undetected and unfixed. The fixes are undoubtedly good for a company with tons of resources. But the response from others about how helpful AI has actually been has been more… meh, after initial fears of an AI-driven vuln-pocalypse haven't really come to pass — at least in terms of actively exploited bugs. After seven months of using Anthropic's Mythos AI model to find bugs in open-source code, VulnCheck says the results are really mixed, and very few bugs seem to be of actual exploitable concern. Krebs also reports Apple, Adobe, Google, and Mozilla also fixed bugs in their various products. More later on Microsoft's cloud collapse (...you noticed?)
More: Bloomberg ($) | The Register | Flying Penguin | @GossiTheDog
~ ~
~this week in security~ is my weekly cybersecurity newsletter supported by readers like you. Please consider signing up for a paying subscription starting at $10/month for access to exclusive articles, analysis, and more.
You can also submit a one-time tip to show your support, or consider gifting a paid subscription.
~ ~
THE STUFF YOU MIGHT'VE MISSED
This dashboard lists all the recent security incidents at certificate authorities
CertKit: After the recent disaster at the now-distrusted certificate authority eMudhra, you can check out all of the past various security incidents at HTTPS-issuers around the world, featuring charts and data.
Spyware attacks trend toward hitting just about anyone
Cyberscoop: New research (and a brutally honest headline) from Cyberscoop showing that use of mercenary (aka government) spyware is now increasingly indiscriminate, as the scope of people who are attacked among civil society is growing wider outside of the usual gamut of targeted individuals — like politicians, journalists, and activists. iVerify tracked some of the recent Apple Threat Notifications, and found a stay-at-home mom and a limousine driver among the recipients. (Also, from my blog bank: Why Lockdown Mode is important for everyone!)
Automakers fix bugs that allowed vehicle location tracking and remote engine start/stopping
Sam Curry: Curry and Shubham Shah found a vulnerability chain in a ForgeRock system (used for handling logins) for two automakers, which when exploited created a valid session for any vehicle owner's customer account. If a customer's car was connected, the researchers could remotely track it and cut the engine. @infosec_au and @samwcyo explain their workings and findings with their usual exquisite detail — and yes, you'll facepalm at the "admin:admin" part.
United blocks AI agents and assistants, citing cybersecurity risks
United Airlines: If you're using an AI agent or assistant, don't expect it to work on United's website any time soon, as the airline is trying to block them from booking flights and managing reservations. The airline says sharing your logins with an AI agent or assistant is a bad idea (correct) as users can't guarantee what their AI assistant will do.
ConnectWise warns of hacking campaign targeting managed service providers
Bleeping Computer: IT management giant ConnectWise has disabled several extensions across 400 or so customer environments, warning that they may have been used in remote access attacks. Security firm Huntress said it's identified at least six MSPs (outsourced IT for many companies) hacked so far, and those numbers are rising.
N-able takes cloud services offline after dozens of zero-days published
SecurityWeek: Remote access firm N-able took its cloud service down and urged on-premise customers take their systems offline after @seankbales dropped some 30 alleged zero-days online. The researcher claimed their past security reports had been ignored and dropped the code online instead. N-able is now back up and, presumably, more secure than before. Huntress has your technical details, while the excellent Bleeping Computer explains for the lay crowd. Also, catch the @breachplease folks chatting about the downstream risk to customers.
GSA scolded for improperly sharing Google Drive links
The Register: The U.S. government's General Services Administration was criticized for leaving potentially sensitive information exposed to employees and staff with no legitimate need to see it by leaving links to Google Drive files mistakenly accessible. The agency's watchdog said that during a "limited search" of GSA"s Google Drive, which has some 2.5 million documents, it found over 116 files containing sensitive information that others could access without needing to. Remember, that's just during a limited search.
U.S. seizes $1.2 billion in crypto from Binance hack
Justice Department: The feds managed to claw back some $1.2 billion in stolen crypto from Binance by freezing it on the blockchain. The DOJ and FBI continue to blame North Korea for the $6.3 billion heist, for which most of it is still in the hackers' hands. A separate North Korean $400 million scheme also got some federal attention by using deepfakes of stolen American identities to target developers in the open-source world — the goal is to hack projects and mass-hack those users.
~ ~
OTHER NEWSY NUGGETS
France oui, Belgium meh on Iran freezer blame: Industrial freezers and refrigerated units keep getting hacked — in some cases with incredible ease, per researchers. Now, French authorities are blaming Iran-backed hackers for the sabotage, while Belgium is a bit more cautious on attribution. U.S. officials are reportedly also blaming Iran, which has denied involvement. (via The Guardian, DomainTools, @MalwareTechBlog)
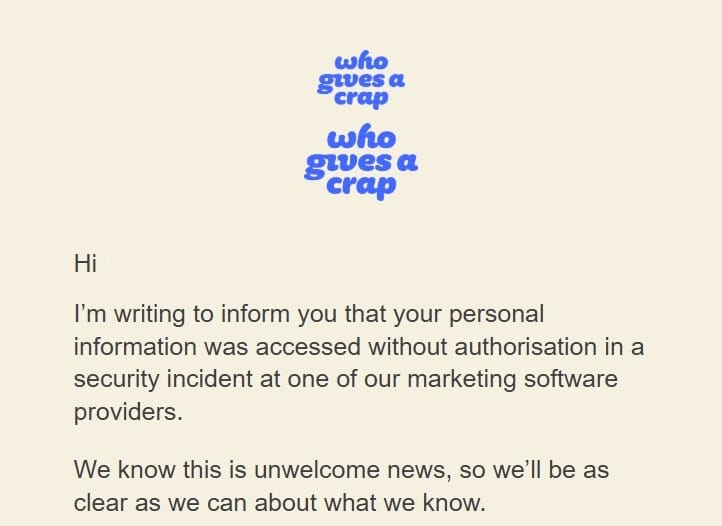
Customer data in the crapper: An amazing headline from The Register about Australian toilet paper maker Who Gives A Crap, which was hacked and customer data stolen thanks to an unnamed U.S. marketing software blunder. (via Australia's ABC)
Quack quack, new CISA leader nomination: The Trump administration has picked Palantir's CISO to head up CISA, the latest attempt by the government to staff the ailing cyber department. It's unlikely to go through during this lame-duck period. Plus, Sen. Ron Wyden isn't likely to let the nomination pass as he's still holding up nominations until he gets answers over telco hacking. (via Cyberscoop, The Record)
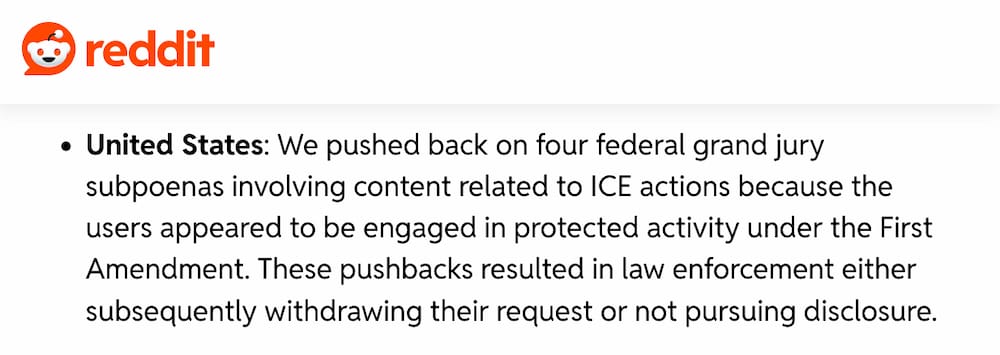
DHS in peak subpoena season: Homeland Security has filed over 185,000 subpoenas (read: not judicially approved!) to seek data from companies, in many cases about critics of the Trump administration. Wired ($) reports how, and I wrote some words this week about how Reddit resisted handing over personal data of people posting anti-ICE content to prosecutors.
Nicking chips from trucks: In also-bad-news for Nvidia… some $11.4 million-worth of company-made chips went missing from a shipping truck between California and Texas. These high-value chips are of particular interest to criminals… FYI, I have more about how hackers help truck and cargo thefts! (via FreightWaves)
Living in wartime Kyiv: Powerful reporting and first-hand testimony from cyber reporter @darynant about what it's like living in Kyiv amid constant fear from Russian rockets and missiles. There are moments of hope, as Ukraine remains the only thing standing in the way of Russia marching across mainland Europe. (via France 24)
Wyndham mum on disclosing lapse: Hotel giant Wyndham refused to say if it'll alert customers that their information was exposed online after the company left a hardcoded credential in its consumer app. (Disclosure: I wrote this story!) The credential allowed access to its member database, potentially exposing millions of members. (via TechCrunch ($), @riana)
Queens Library recovering from ransomware: A ransomware attack hit the Queens Public Library in NYC last week, knocking out services across much of the borough's locations. Some services are now recovering. (via @AlesandroOrtiz)
Microsoft's cloud took a snow day: Microsoft is on the apology tour after a day-long outage nuked Outlook, Teams, Defender… and practically it's entire cloud due to a technical fluff-up, and not related to a cyberattack or AI screwery. As of Saturday, things are back to normal — so, Outlook still functions terribly, lol. (via The Verge ($), TechCrunch ($), CNN, @hacks4pancakes, @katie-drummond, @eldomador)
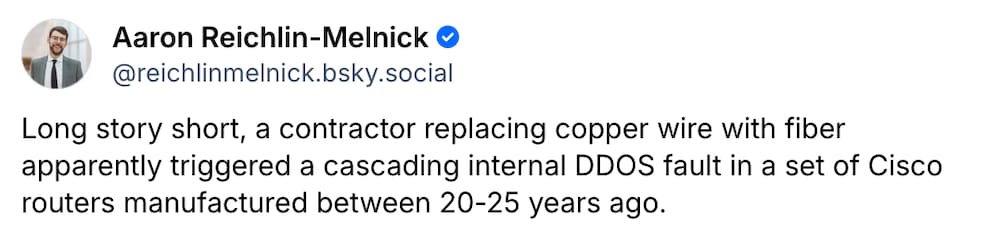
So did the U.S. skies… A rare U.S. nationwide ground stoppage on Friday afternoon froze air traffic and halted departing flights for hours following a communications error, sparked by contractor L3Harris upgrading copper wiring to high-speed fiber while replacing a router… yes, at peak travel time... (I know, I hear you.) Secretaries of DHS and Transport still don't know what ultimately caused the outage, but can't seem to escape the shadows of their own incompetence. CBS and rud.is have the technical details, as does Reuters' ($) in-house aviation nerd (love it), and CNN and BBC have ongoing updates. And, @davidshepardson has a statement from L3Harris.
~ ~
Quick mention: 🚨 If you're interested in sponsoring ~this week in security~, please get in touch! I have sponsorship slots open for the remainder of 2026, and into 2027. Lock-in before end-of-year for a 10% discount! 🚨
~ ~
THE HAPPY CORNER
Hoo-boy! I have a very fun happy corner for you this week. It's a belter, so buckle up, let's blast through some fun things to lighten the mood. *breeeeeathes in* ...here we go!
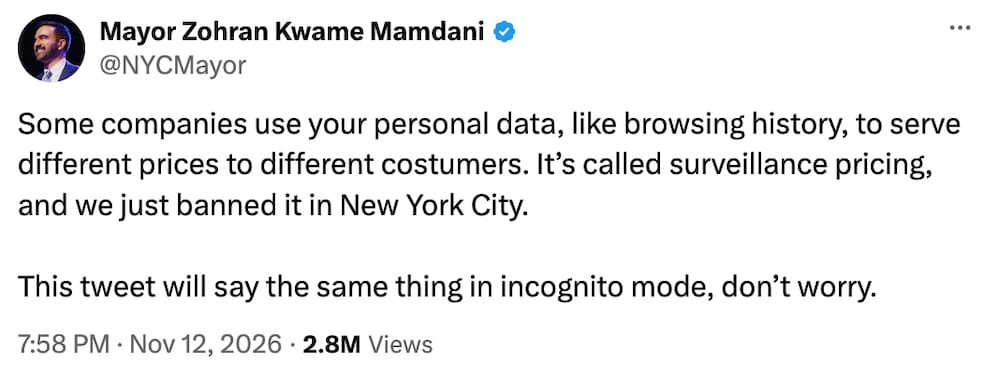
Nevada named its first statewide privacy and data protection officer, the latest state to lean into protecting citizens' privacy and data rights, huzzah!... Safari browser gets a new privacy control feature so users (theoretically) never have to see another cookie banner… and New York City passed a ban on companies and stores setting prices that rely on personal data — yes, it's gross, but now it's banned across the city. Another huzzah!
Also in New York news… the only breach that you'll absolutely love to see: a whale was spotted in the Hudson River! (via The New York Times ($))
And we're not even close to being done with this week's good stuff...
Major congrats to the incredible Dr. Tarah Wheeler, who successfully defeated one hell of a thesis and earned a doctorate in machine learning from the University of Oxford. As a friend, I couldn't be prouder. This is a huge achievement!
Meanwhile… in remote printer hacking… ♪♫♩ Never gonna print you up… never gonna print you down…♩♫♪ And not to be outdone, hacking an air purifier to avoid the cloud sounds like fun.
Google nerds pointed one of its most advanced DeepMind AI models at Signal's code to see how secure it was and… yep! Security confirmed, per Wired ($).
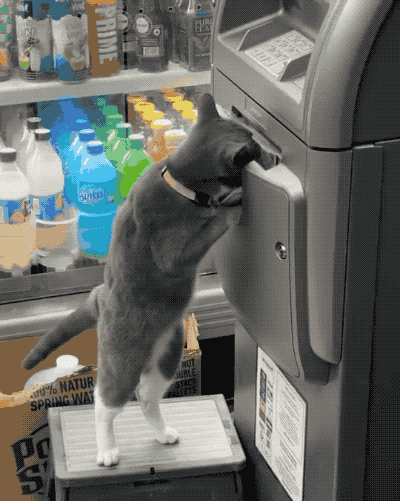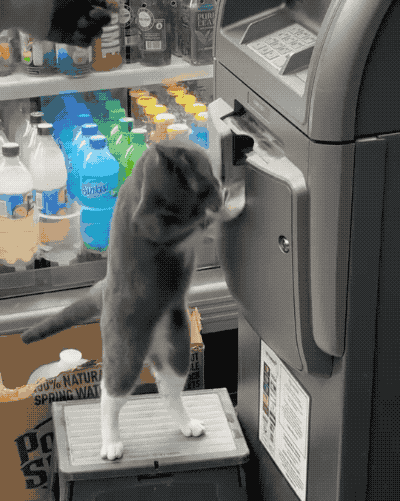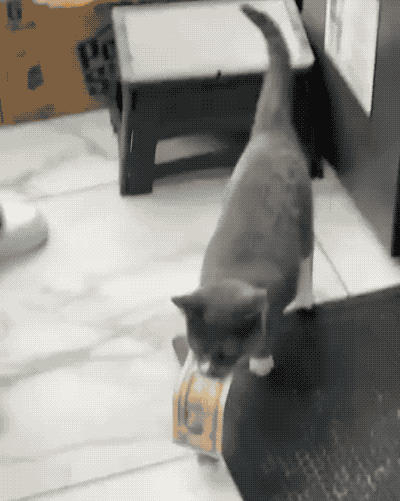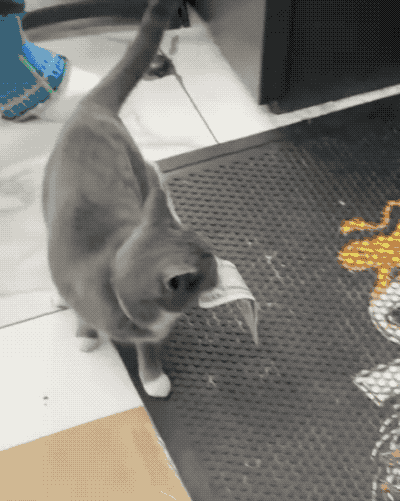
A rare jackpotting attack seen in the real-world:
And, take some advice from @cybersecmeg. You can't escape from all of your problems in cybersecurity, but jumping out of a plane is one way you can. Remember to take time for yourself!
Have good news to share? Get in touch! this@weekinsecurity.com.
~ ~
CYBER CATS & FRIENDS
This week's cyber-cat pupper is Bear, who can be seen here taking a relaxing moment to touch grass (literally) after a busy week in cybersecurity. (I want to boop the snoot so badly!) Thanks so much to Leigh for sending in!
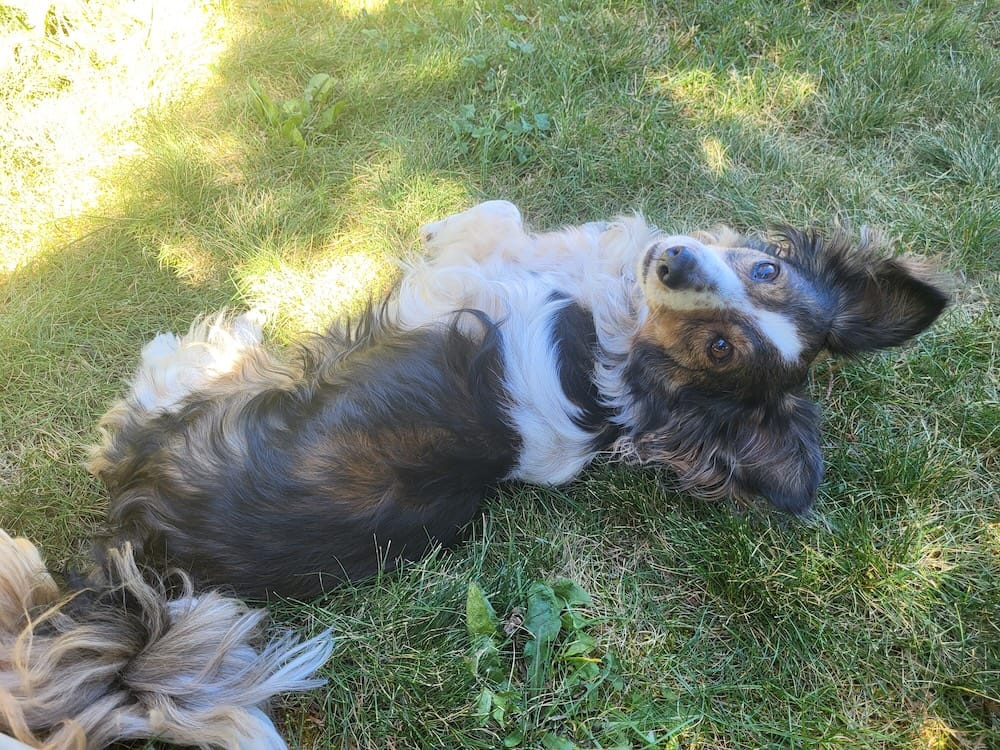
🐈 ⭐ Please send in your cyber cats! ⭐ 🐈⬛ Drop me an email with a photo of your cat (or non-feline friend) and their name and they'll appear in a later newsletter!
~ ~
SUGGESTION BOX
Are we done? *looks around cautiously* Going once… going twice… OK, let's call this week that was! Thank you so much for making it through this busy edition. I appreciate you reading and supporting this newsletter.
If you liked this week's newsletter, please share it! As always, you can reach me by email with any feedback, comments, questions, and other tidbits of next week. I'm also on Bluesky and Mastodon as well.
Back next Sunday as usual. I'll catch you then.
Ta-ra!
@zackwhittaker