this week in security — november 22 2026 edition
THIS WEEK, TL;DR
Outages keep piling up, or are we just noticing them more?
~this week in security~: So… about those outages! Last week, we saw Microsoft's big cloud fail and the U.S. skies grounded for hours… then this week, the NSA's classified network went down for days, Apple's logins were briefly broken, Chase bank had a brief hiccup, and United Airlines had an outage separate to the unscheduled sky chaos. What ties all of these together? Not cyber… but rather decades of technical debt piling up and snowballing into these monster incidents that are increasingly difficult to detangle, thanks to years of underinvestment in modernization — but, oh! I'm so glad that executives keep getting bonuses (extreme sarcasm). But as financially motivated cyberattacks increasingly seek to cause disruption, it'll be easier for hackers to cause outages by knowing exactly which rickety systems to target, while AI is undoubtedly making some hacks easier, especially when faced with weak security defenses. The use of AI to find and patch systems at speed before malicious hackers is also breaking things. All the while, the U.S. government admits these outages have little to do with cyber, Trump still fired national cyber director Sean Cairncross, who did so resoundingly little during his brief tenure that we'll barely notice he's gone. Wired ($) has a great explainer on how to know if something is an actual outage. Since these'll keep happening, save a bookmark!
More: The New York Times ($) | Reuters ($) | Financial Times ($) | WSJ ($) | Axios | Nextgov | TechFinitive | Little Flying Robots | WNYC | @dustinvolz | @JenGriffinFNC
Web giant Optimizely hacked to deliver malware to over 170 popular websites
Report URI: Astoundingly good findings by @scott_helme who helped to identify over 170 websites that had been compromised by a breach at Optimizely, a company that allows websites to run online tests and customize their experiences. Hackers modified a JavaScript file embedded to deliver malware on customer websites, including BBC, CNN, Ledger, and Zoom. The malware was capable of stealing screenshots, cookies, session logins, and crypto. Some of the malware samples delivered DarkSword and Coruna spyware, which can hack iPhones without any user interaction. Optimizely published its own post-mortem [PDF]. Krebs On Security has your full run-down of the incident, which could have been broadly mitigated if websites had content security policies (CSPs) in place that block third-party domains. Also, another great reason to use an ad-blocker.
More: Bleeping Computer | Ars Technica | NL Times | CSO Online | The Record
British former-teen hackers face jail for Scattered Spider hacks
BBC News ($): Two British cybercriminals who hacked their way through their teenage years are both facing lengthy prison sentences for their attacks. The hackers were part of a roving group of advanced persistent teenagers like Lapsus$ and Scattered Spider, among others, which tore through the web with social engineering attacks and stealing data as they went. Tyler Buchanan, 24, from Scotland was sentenced to six years in a U.S. prison after his extradition for his role in hacking big companies. Meanwhile, Arion Kurtaj, 21, pleaded guilty to a ton of hacks, including Uber and the breach involving the game maker of Grand Theft Auto 6, after initially deemed unable to stand trial.
More: BBC News ($) | Justice Department | Crown Prosecution Service | The Record | SecurityWeek
FBI hacked (again!), Dept. of Agriculture payments system also breached
CNN ($): Not a great look for the FBI, which got hacked for a third time this year after hackers breached its national law enforcement database, NCIC, used by police departments for tracking warrants, criminal record histories, fugitives, and missing persons. It's unclear how much damage was done, but all eyes are on whether any data was exfiltrated (which would be of no doubt useful to criminals and others). Trump said the breach was "not good," or Understatement of the Week™. We'll no doubt learn more about this as the week rolls on. Also, uh, the Department of Agriculture's system for paying farmers was hacked, prompting the government agency to take some systems offline. I'm losing track of how many times the government was hacked this year… If only the U.S. had a fully staffed cybersecurity agenc… Oh… wait!
More: Bloomberg ($) | NBC News | Nextgov
~ ~
~this week in security~ is my weekly cybersecurity newsletter supported by readers like you. Please sign up for a paying subscription, starting at $10/month, for access to exclusive articles, analysis, and more.
You can also submit a one-time tip to say thanks, or gift a paid subscription.
Recent blogs include: Reddit resisted giving users' personal data to the U.S. government over critical ICE posts | Phony visa application and passport sites face U.S. government crackdown | Residential proxies found at the White House
~ ~
THE STUFF YOU MIGHT'VE MISSED
Microsoft blames day-long Outlook outage on July bug
The Register: Microsoft blamed its recent email and broader cloud outage on a trifecta of issues, including a bug that was introduced in July but went undetected until things started to go wrong last week. Microsoft AI boss @clamanna has the post-mortem.
AI supply chain is exposing people's prompts and secrets
Ars Technica: Researchers planted some two million digital tripwires (aka canary tokens, which are designed to alert you when they're exposed or accessed) in AI requests to see how leaky the network of interconnected pipes, tubes, and routers of the sprawling AI network is — and they found that it was a hot mess of upstream leaks. The findings suggest that hackers are siphoning prompts from at least three AI providers and apparent false claims regarding "zero" data collection. Also… check out Micah Lee's latest guide on using open-weight models that you can run yourself, no big AI giants needed. It's a handy start for AI newbies.
Meta staff warn of early security and privacy mishaps with Muse AI
Reuters ($): Also, in horror stories: Meta's own employees raised alarm bells about the now-popular Meta's AI assistant Muse, who reported receiving other people's bank balances and details about smart home tech that didn't belong to them. Some of these flagged issues are downright creepy, like randomly and without prompting mentioning things like money laundering for no reason whatsoever. 👀
Artex AI used to hack ConnectWise, Barracuda, and South Korea's finance industry
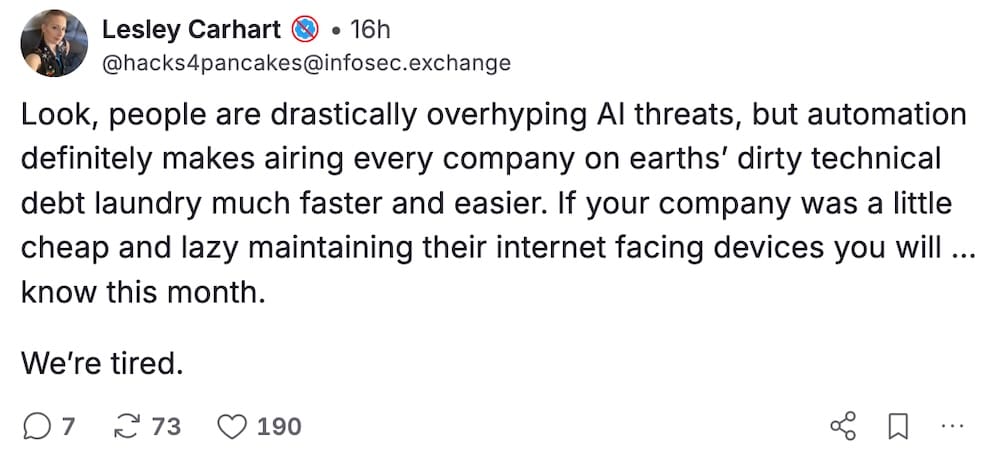
TechCrunch ($): Aside from getting hacked, the FBI also had time this week to warn about a spate of AI-related hacks that rely on the autonomous AI hacking toolkit Artex (among others, like Cairn). These hacks often exploit low-hanging security flaws but with incredible speed. (Disclosure: I wrote this story!) Among the victims of Artex hacks include remote access firm ConnectWise, security giant Barracuda, and recently AI company Bitrise, all of which were breached by way of exposed passwords, lacking MFA, or similar basic issues that AI finds easy to exploit. This trend shows that doing the security basics will really help with your overall cybersecurity posture. Listen to @hacks4pancakes!
U.K. scrambled to fix refrigerator flaws amid mass-hacks
BBC News ($): While refrigeration units across France and Europe were being hacked and sabotaged to spoil food and other critical frozen goods, the top blokes at Pen Test Partners helped raise the alarm about a similar major security flaw in Omega-made internet-connected fridges across the United Kingdom. Working around the clock, the researchers got thousands of affected fridges offline and patched before attackers could cause similar damage to British freezers.
New Java4Shell bug can allow remote code execution, patch today
The New York Times ($): Security researchers at Calif (of recent PHP-ocalpyse fame) found a bug in Java, the aging web language used for decades and is therefore everywhere, which can be exploited to gain remote access to a vulnerable system running the software. The bug can be triggered by overloading its memory by sending 64 "A" characters followed by one equal sign, which is base64 for… well, pretty much just screaming in computer speak. CISA, for what it's worth, urged everyone to patch. Not to be outdone: A new bug called nginx2root may allow unauthenticated attackers to remotely run malware on vulnerable web servers running nginx. All to say, again, just patch your stuff (and web servers, if you have them!), and all should be fine. IFIN has your back, and Censys and Wiz have more on the risk.
Tor fixes bug that allowed relays to be flooded with traffic
Tor Project: Also, if you happen to run a Tor relay (for allowing users to access the Tor anonymity network), upgrade today to fix a bunch of fixes, and a new denial-of-service defense to protect against a recent flood of DDoS attacks targeting the global network.
Some Visa, Mastercard, and Chase customers had personal data stolen
Cybernews: An extortion racket stole personal data about high-net-worth individuals who bank with JPMorgan Chase (entirely unrelated to its recent outage) from a third-party that provides marketing services to the bank. The data included names, email addresses, and in some cases phone numbers of about 16,000 people. A few Visa and Mastercard customers also had some data leaked in the incident, per The Verge ($).
~ ~
OTHER NEWSY NUGGETS
Coles hacked down under: Australian supermarket chain Coles declared a cybersecurity incident — and didn't really say much else about it! There's no indication of a data breach (yet) and stores are open and online is working. Aussie media don't seem too convinced by the whole situation, so I'll keep an eye on this. (via Australia's ABC, ACS)
Dutch wary of pervert glasses: The Netherlands' privacy watchdog urged Dutch consumers not to buy smart pervert glasses that constantly record other people without their permission. In true pervy form, the authority said that in their tests the smart glasses "devices advised a user on how to date a child," and in other cases misread a medicine bottle, and claimed to have called an ambulance when it hadn't. (via BBC News ($))
Hackers steal Entra admin info: Microsoft admitted a breach where hackers gained unauthorized access to administrator email addresses and other tenant configuration information of Microsoft 365 accounts. The hackers obtained the data by exploiting a bug in its Entra Connect Health, a service for monitoring clouds. (via Bleeping Computer)
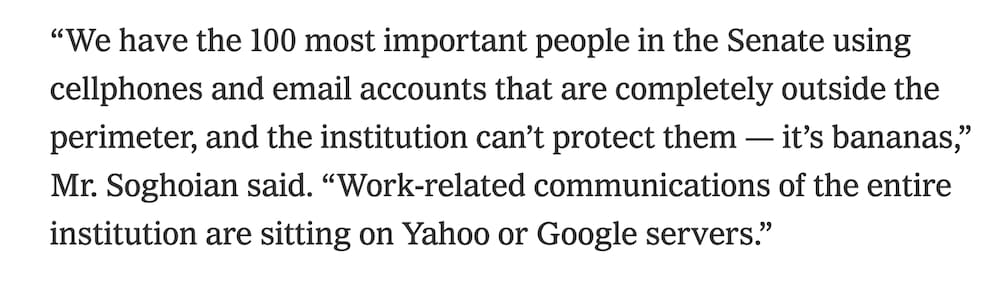
Lawmakers warn of Trump data threats: The Trump administration has long targeted its critics, including war crimes investigators and ICE protesters. But since winning the mid-term elections, Trump has centered his attention on Democrats who took back Congress and can now investigate his corruption. Per the NYT ($), one Democratic senator is warning lawmakers to take actions to secure their communications, especially since Trump targeted lawmakers' phone logs during his previous go in the Oval Office.
Apple finally gets to reveal secret order: Apple finally spoke after the U.K.'s surveillance court ruled that the company is now allowed to disclose that it received a secret court order issued by the U.K. government … which we all knew about because it already long leaked to the press. The order demanded a backdoor for accessing encrypted iCloud data, but Apple refused. Apple told me that it "welcomes the decision" to finally disclose the existence of the order. (via MacAnorak, Liberty International)
Infoblox blames breach on vendor: Network security firm Infoblox confirmed a third-party breach allowed cybercriminals access to its SharePoint server, including a wealth of data about customers. The data also included employee information. (via The Register, TechCrunch ($))
Major data breach hits France: A breach of French postal subsidiary Maileva exposed the names and addresses of 22 million people. The breach has been called one of the largest in France's history. (via DataBreaches.net. Actu.fr, Infosecurity Magazine)
~ ~
THE HAPPY CORNER
Welcome back to the happy corner, the premier place of peace and calm in the Sunday newsletter space. Leave your stress at the door. (Also, this is a shoes-off happy corner.)
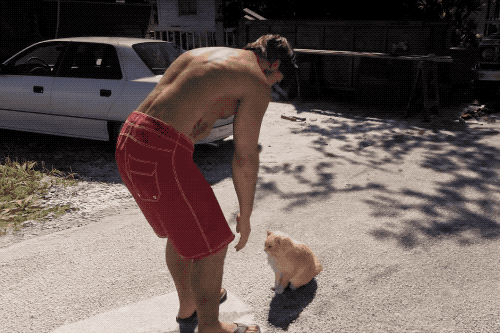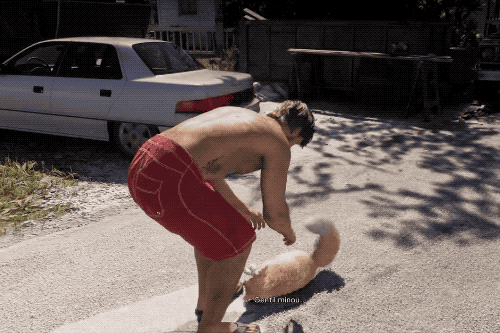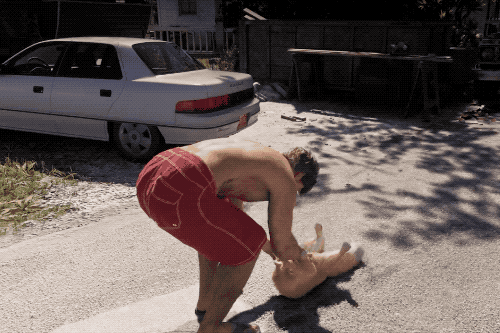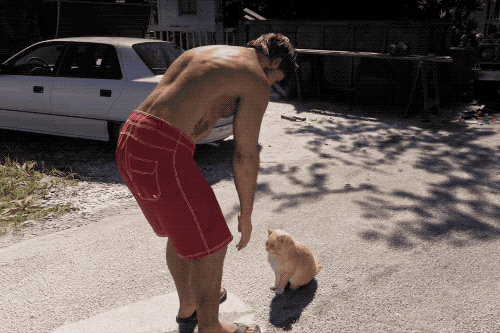
Alright, let's go check in and see what Grand Theft Auto 6 players have been up to this week… Since the long-awaited game is now out, some folks have been a bit distracted! A big feature in the new carjacking and crime game is the ability to say hello to cats and pet them… (maybe I should get this game?)
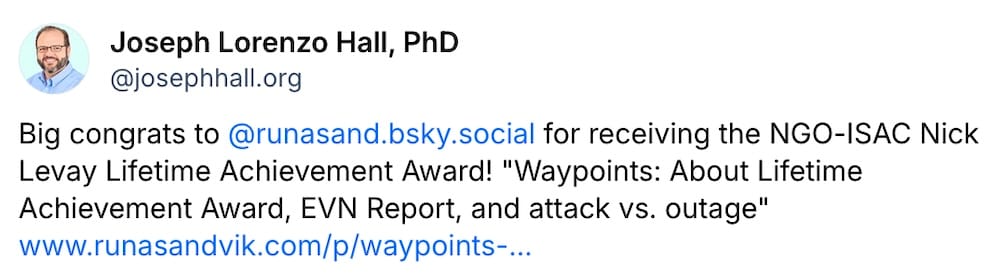
A huge congrats to the cybersecurity extraordinaire Runa Sandvik, who received the NGO-ISAC Nick Levay Lifetime Achievement Award for an incredible career helping others, especially at-risk folks, to defend against digital attacks. Amazing stuff and well deserved. (via @josephhall)
Apple rolled out a new system-wide permissions setting for macOS users, replacing its Full Disk Access setting, which had been long used by AI agents to access data on a person's computer. Apple said this was bad for security and privacy, so changed it.
A new edition of Phrack is now out. I'm very excited to brew a pot of coffee and dig into some extreme nerdery this weekend. The last edition was out in August 2025, so we've been overdue.
I really enjoyed this Mastodon thread by privacy expert @Em0nM4stodon with folks recommending their favorite privacy-enhancing technology. There are a ton of ideas and suggestions in here, as well as some staple favorites (like Signal and Privacy Badger!).
A reader emailed in to ask about book recommendations. At TechCrunch ($), we have a running list of cyber books that we like (and probably due for an update), and Cyberwire has a few suggestions. Do you have any top recommendations to suggest? Get in touch with your favorites, and I'll wrap up your favorites in an upcoming newsletter.
Meanwhile, @harrison.page wasn't happy about having his garage door app spamming him with ads, so got mad in the most delightful and productive way by hacking and replacing the app altogether. Excellent stuff!
OK, let's check in one last time on the Grand Theft Auto cats… oh, and I heard there's a hidden dog on a jetski that'll take you to a secret island… (maybe I need a PlayStation?)
Have good news to share? Get in touch! this@weekinsecurity.com.
~ ~
CYBER CATS & FRIENDS
This week's cyber-cat is Mr. Garfield, who won the cyber capture-the-flag contest before his furry friend Leopold and so gets to snuggle on the extra fuzzy blanket. Thanks so much to Kenn W. for sending in!
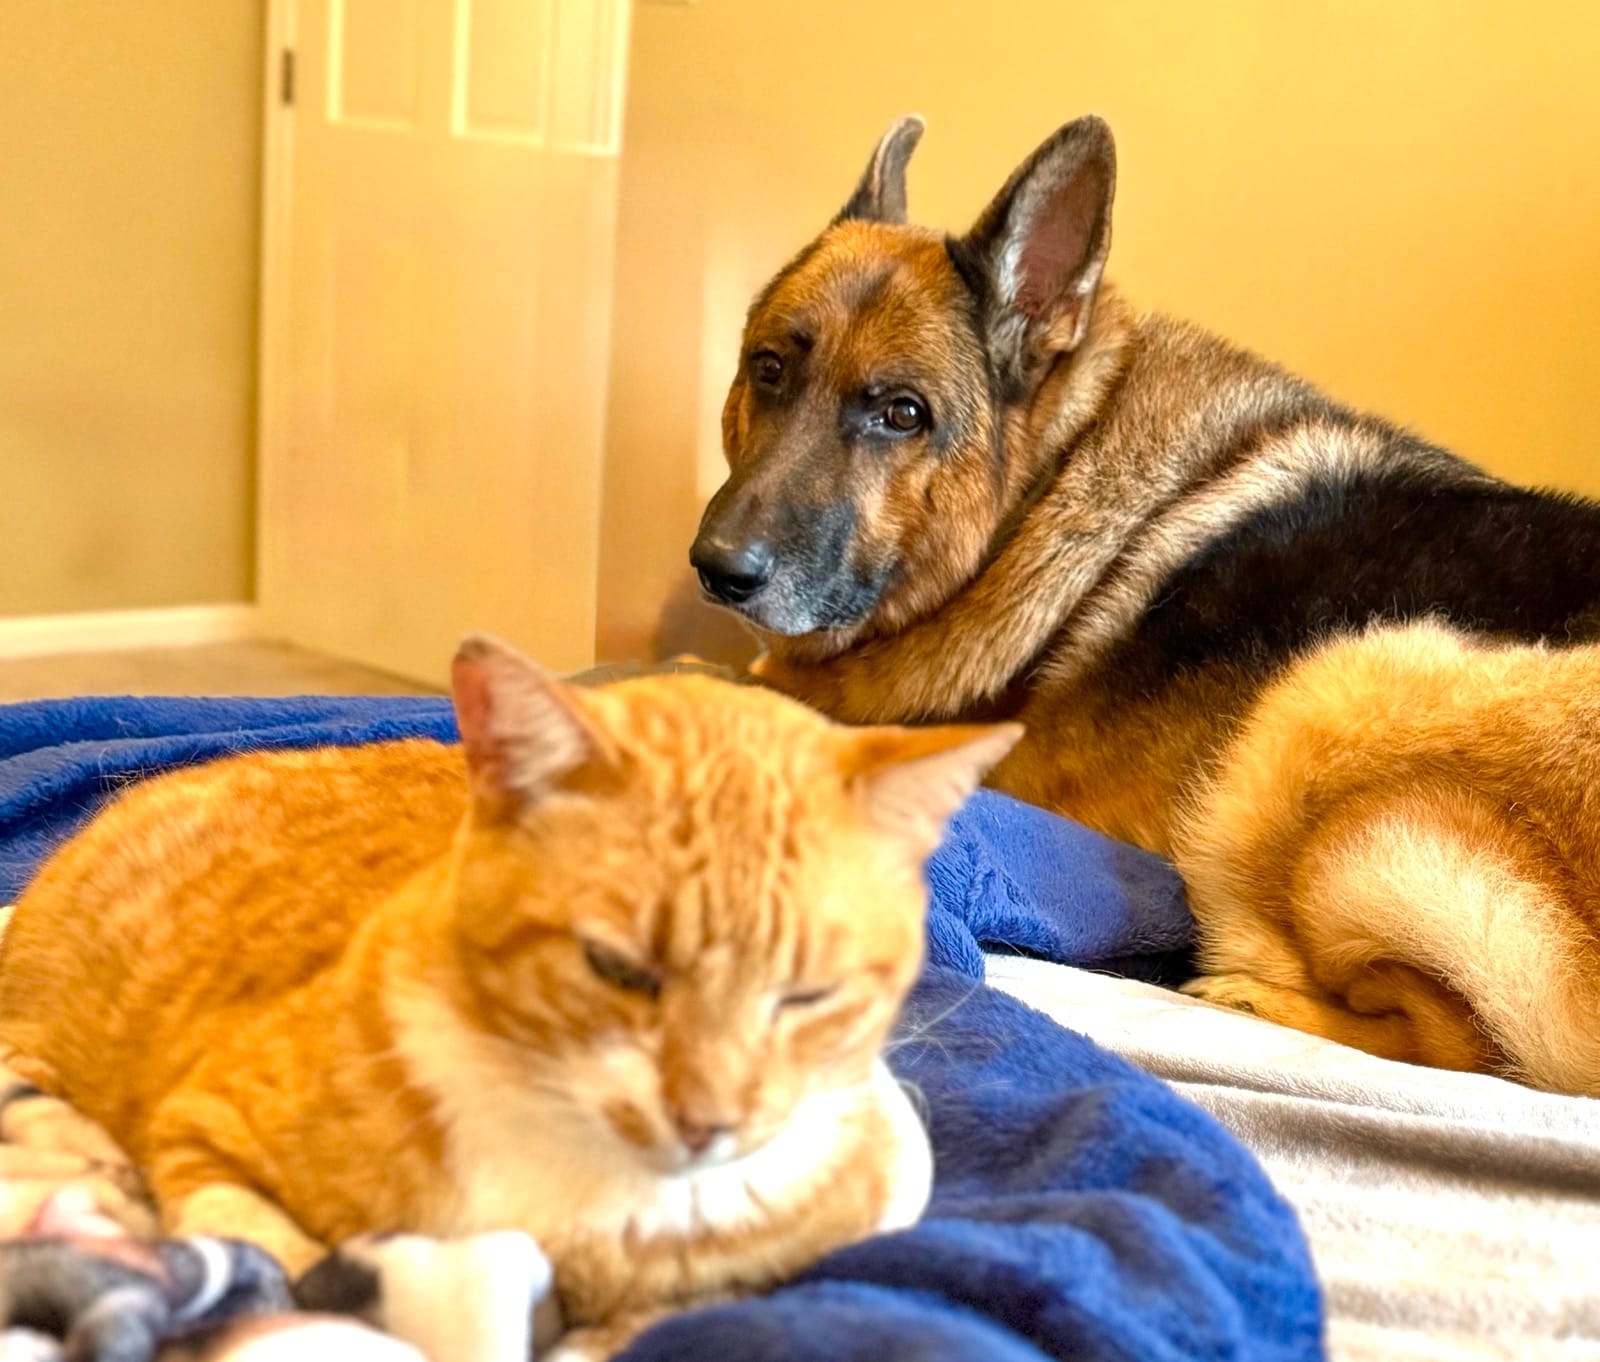
🐈 Send in your cyber cats! 🐈⬛ Drop me an email with a photo of your cat (or non-feline friend) and their name and they'll appear in a later newsletter! (Extra credit for anything holiday-themed!) If you've sent in before, I'd love an update!
~ ~
SUGGESTION BOX
That's it! No more security news this week, I'm calling time at last! Thank you so much for reading, subscribing, and supporting the newsletter. Every week I get the privilege of writing this and sending it out to thousands of you, and I'm honored that I can be a part of your routine.
As the news gets messier and more complicated, a lot of work throughout the week goes into this newsletter and blog, and it's certainly an ongoing effort to make sure that you get all the news you can use, without any of the noise or junk. If you find this newsletter helpful, please consider a paying subscription (or if your company wants to sponsor!).
It also really helps to share this newsletter on your ~social media~! It's really appreciated. As always, you can reach me by email with any feedback (really!), comments, questions, and other tidbits of next week. I'm also on Bluesky and Mastodon as well if you want to tag me in things.
Next week might be a little lighter than usual for the U.S. Thanksgiving break… (or not — who knows!)... but let's hope for a quieter one so that we can enjoy a few much-needed days off.
Until then, I'll catch you next week, cyber friends!
@zackwhittaker